
IoT Security Isn’t a Feature. It’s a Series of Decisions Nobody Remembers Making.

- Sep 24, 2026 |
- By Gaurav Harkhani - Bluepixel Team

IoT Security Isn't a Feature. It's a Series of Decisions Nobody Remembers Making.
If you ask most product teams at what point in an IoT implementation security is considered, the truthful response is: once the demo is functioning. When you have a device that hooks up, streams the data, appears on a dashboard - that's the moment the team stops to ask about authentication, remotely-upgradable firmware, or whether the device can be reprogrammed after a thief finds a spare - all architecture effects that are now sitting right there, having been made by default.
Here's the issue with security in IoT devices. It's never the last mile. It is always the defaults that nobody returns to - the API key everyone bootstrapped in and has not changed, the debug port left open because the factory had to be able to access it, the update server that allows any image that looks close enough. No one remembers building those; they are just always there.
Why IoT security gets deprioritized in the first place
Teams building a web app have decades of shared convention to lean on: TLS everywhere, OAuth, mature auth libraries, managed identity providers. IoT doesn't get that shortcut, because "IoT" isn't one thing.
| Device class | Typical constraints | What dominates the threat model |
|---|---|---|
| BLE wearable | Coin cell or small LiPo, tiny flash, phone as gateway | Pairing security, tracking and privacy, the companion app as attack surface |
| NB-IoT / LTE-M field sensor | Years on one battery, expensive bytes on the wire, unattended deployment | Physical access, long unpatched lifetimes, identity on a carrier network |
| Industrial gateway | Mains power, Linux-class hardware, bridges OT and IT networks | Lateral movement into control systems, remote access, patch windows tied to uptime |
Advice that's correct for one of these is often wrong for another. Generic "IoT security checklists" tend to be either too vague to act on or wrong for your device class.
The deeper issue is cost. Security on embedded devices is paid for in currencies teams don't budget for. A TLS handshake over a constrained radio costs battery. A second firmware slot for safe updates costs flash. A secure element costs a line on the bill of materials, multiplied by every unit you ship. Every security decision on a constrained device trades against the resource the product needs to work, and that's why security keeps losing to feature deadlines.
The answer isn't to do everything. It's to make the small number of decisions that matter, deliberately, while they're still cheap to make.
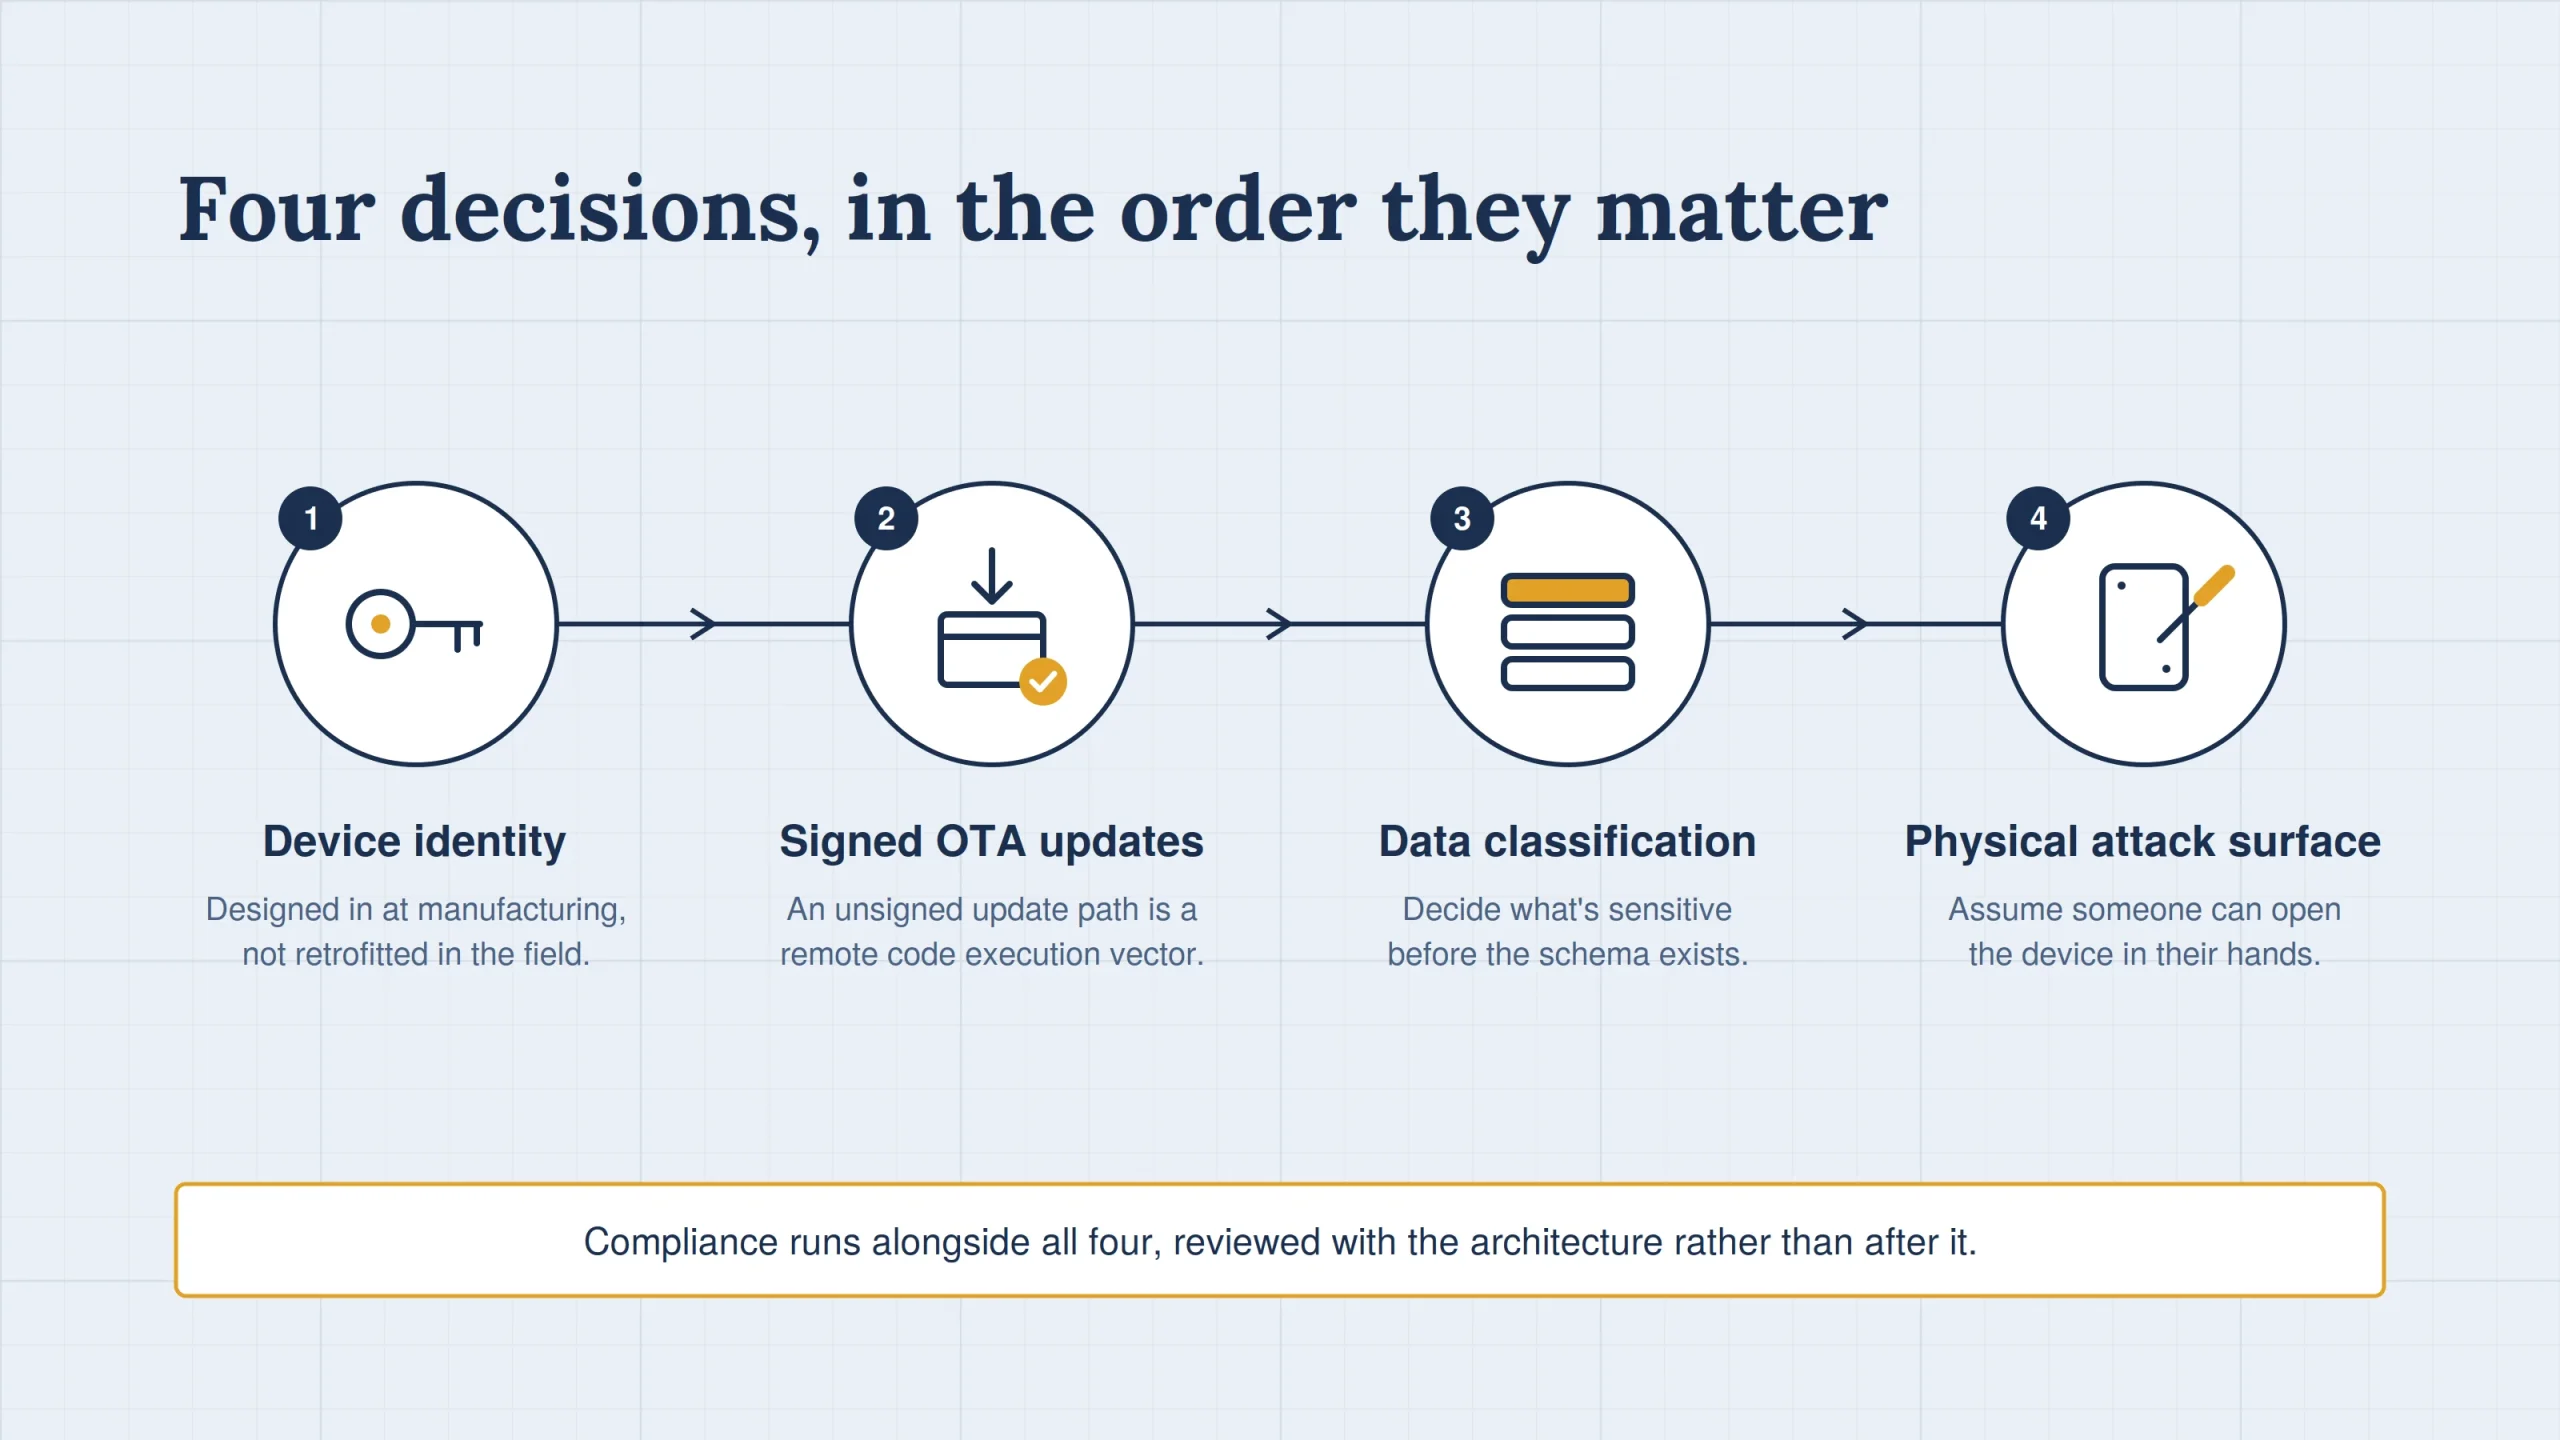
The decisions that actually matter, in the order they matter
1. Device identity, before anything else
If a device cannot cryptographically demonstrate that it is indeed what it says it is, then nothing built on top of that connection, nothing that transit that connection, be it the data, the command channel, or the OTA system can be considered trustworthy.
In reality, good device identity would be:
- What about the key? A distinct key pair for each device. It should be generated within the device, with the private key stored in the secure element (preferably) or the hardware protected key store of the MCU, such that the private key never appears outside it.
- A device certificate from your own CA that was created during manufacturing Your device is authenticated by the cloud by mutual TLS (or other method) instead of sharing a secret.
- The factory isn't a place you can bypass a provisioning process that allows devices to get out into the world. That means storing everything in a way that's easily auditable and in such a way that your compromised production line can't create authentic identities.
- A way to cut the cord. When a stolen, return or cloned device passes through, you must be able to disconnect that single device without disconnecting everything else.
The anti-pattern is the fleet-wide credential: a single API key or one symmetric key burned into every device. It's quick to deploy and it locks every device into a monolithic key.
It has to be baked in at manufacturing time. Applying identity to units already in the field is one of the priciest errors in IoT, and one of the most prevalent. Once you ship devices without hardware root of trust, you're out of luck - you're not upgrading one with a firmware update.
2. Update capability, treated as a security feature
Here's an example: Not being able to patch a device remotely isn't just frustrating - it's a ticking time bomb. Every one of these unpatchable units is a ticking liability the moment a flaw is identified in your code, RTOS, BLE stack, or in a third-party library that you didn't even know you were dependent on.
More than just an update path Not only a good idea to have an update path, but even more of a good idea to consider is: what if the update channel itself is compromised? An OTA mechanism without signed firmware is a remote code execution path with a much more memorable name.
A production-grade update path typically includes:
- Each of the keys used to sign the firmware must be stored out of band, on an HSM or other similar environment and not on a CI runner or a developer's workstation.
- Verifying the signature of an app on the device, even before any image is launched. Verifying the image in the cloud is no replacement.
- Anti-rollback protection: So that an attacker can't "update" a device to a previous compromised release.
- A/B partitions or another recovery mechanism in case the update fails / is interrupted - this prevents a bricked unit. A device that bricked on update will soon have updates turned off by an ops team that got burned.
- Staged releases with health reporting if say a bad release hits 1% of the fleet instead of 100%.
Think of the update path as fundamental infrastructure. It should have its own testing, monitoring, and incident plan-because that is the one thing you're going to rely on when everything else has failed.
3. Data classification before data collection
Not all telemetry carries the same risk. A soil-moisture reading and a patient's heart rate both look like "sensor data" in a database schema. They carry entirely different regulatory, contractual, and reputational weight.
Classification is the simple step that makes everything downstream tractable. Most projects need only three or four tiers, for example operational telemetry, personal data, sensitive or regulated data, and security material such as keys and tokens. For each tier, decide:
- where it may be stored, cached, or replicated, including the region;
- whether it can appear in logs, crash reports, or analytics pipelines, which is where sensitive data most often leaks;
- how long it's retained, and how it's deleted;
- whether it needs to leave the device at all. The cheapest data to protect is data you never collect.
This has to happen before the schema is designed, not during a compliance review six months before launch. Once personal data is flowing into a general-purpose telemetry pipeline, separating it out again is a migration project, not a configuration change.
4. The physical attack surface, which software teams routinely forget
A device on a field, on a factory floor, or in a public place can be physically disassembled. If you can dump the firmware, keys, or credentials off of a device that someone can physically hold in their hand, your defense in the cloud is protecting a device that has already been compromised at the edge.
The questions to ask are concrete:
- Are the production devices more difficult to operate, disable, or lock out the debug interfaces (JTAG, SWD, UART consoles, etc.)?
- Is flash readout protection enabled, and is external flash encrypted?
- Is the device doing secure boot so tampering with the firmware (and being able to write to flash) won't mean it will run?
- Are they just secrets sitting in plain flash where someone with a $30 programmer can just take it out?
Then if you break one unit, what do you get? One device, or the entire fleet? You see where the per-device identity from decision one comes into play.
You're not going to prevent a well-funded lab from trying to hack your physical hardware. What you want is for physical access to a single unit to be a localized issue and not a systemic one.
Where compliance actually bites
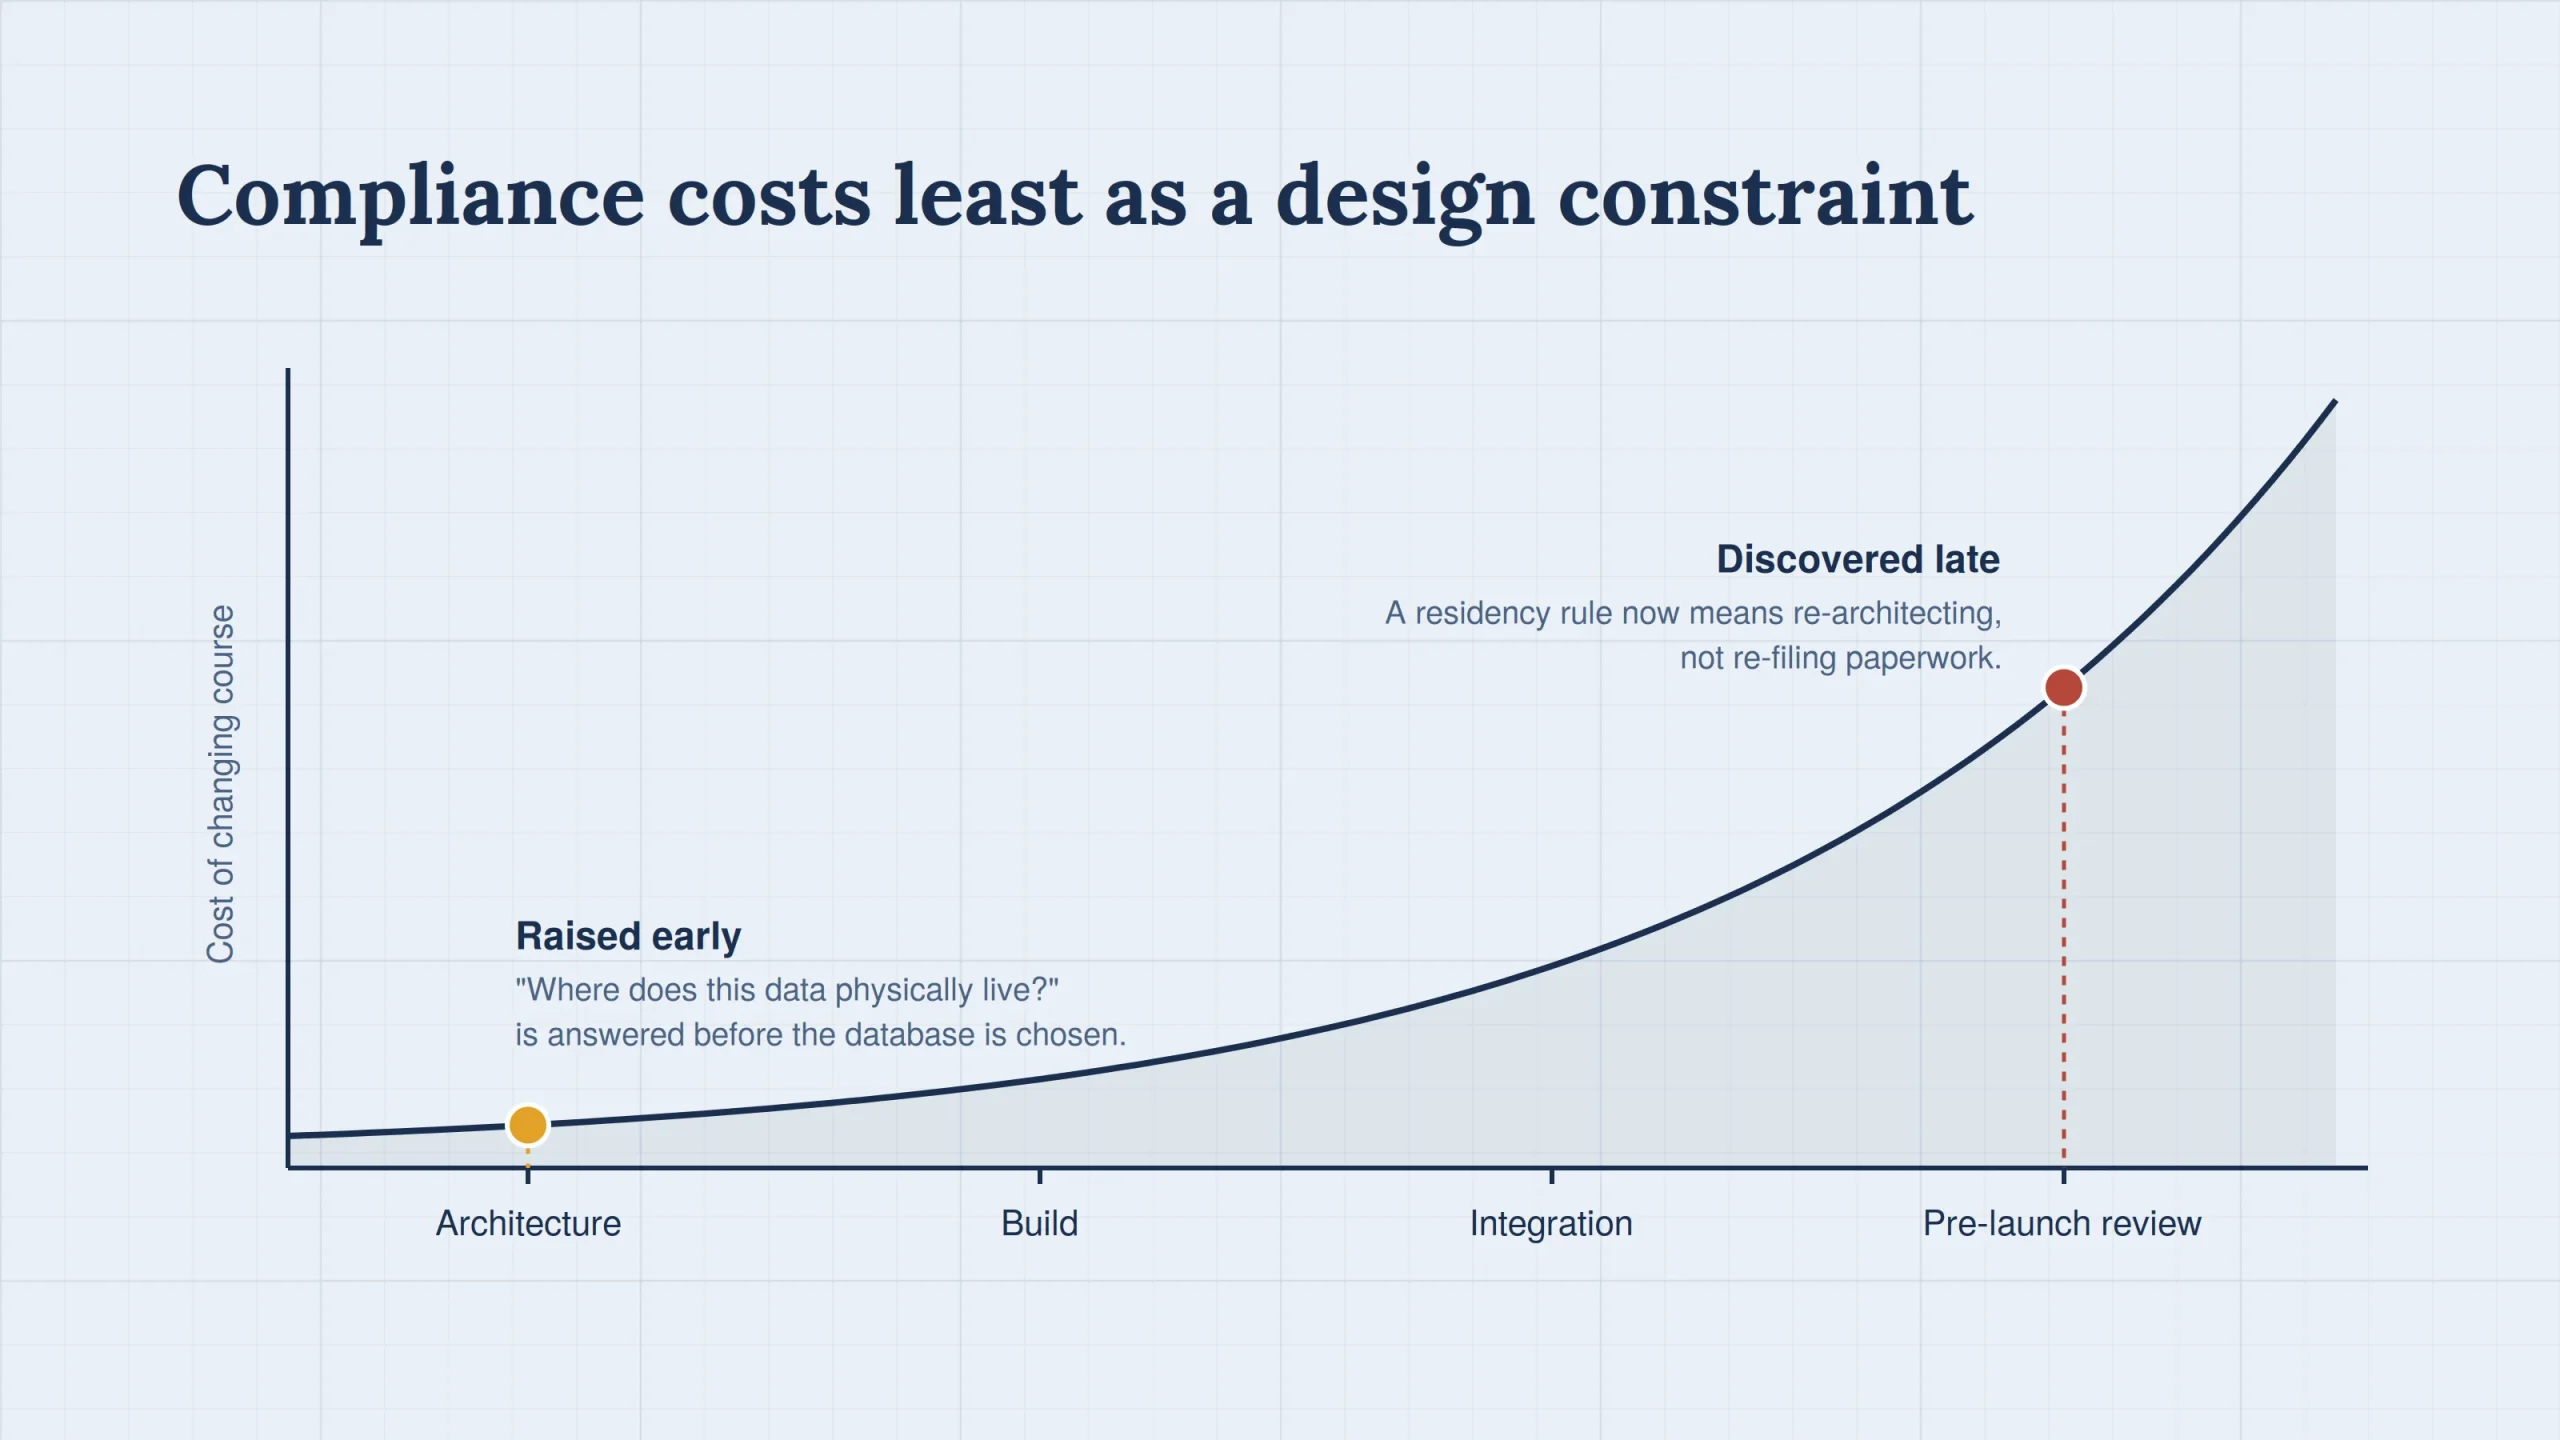
Regulatory requirements don't often fail because of an individual's lack of knowledge of the requirements. They fail because compliance becomes a documentation exercise, not a design constraint.
Over the same period, the connected device regulatory environment has also gone from "siloed" to "cross-cutting". Medical and industrial device teams have been operating with their own cybersecurity standards such as HIPAA and IEC 62443 respectively, alongside consumer-focused ones like ISO 27001. Consumer and general-purpose device teams now have cross-cutting rules to contend with too. UK product security regulations, for example, prohibit "out-of-the-box" default passwords and require a disclosure policy and minimum support window; the new EU Cyber Resilience Act is gradually introducing security-by-design, updating and vulnerability processing requirements for products containing digital elements sold in the EU; and standards like ETSI EN 303 645 provide a helpful, practical baseline that dovetails neatly with many of these rules.
Observe how well these requirements follow the decisions made above: unique credentials, a real update path, a definite support lifetime, a way to report and address vulnerabilities. Whenever teams explicitly made these decisions, they learned that compliance was largely a matter of proving they had met the requirements. Teams who had not explicitly made these decisions learned that compliance was a matter of redesign.
Data residency is the silver-bullet late discovery requirement. Is a mandate that health or personal data resides in a specific region discovered after the cloud architecture is built? It typically results in the re-architecting of storage, backup, logging, and-sometimes-even vendors. The solution is cultural, not technological: involve compliance requirements in the conversation early enough that "where does this data physically live?" is settled before the database is chosen.
What good IoT security actually looks like in practice
It isn't a hardened product with every possible protection bolted on. That isn't achievable within real power and cost budgets, and pretending otherwise just produces security theater. It's a small number of foundational decisions made deliberately, early, and revisited as the threat model changes:
- Device identity established at manufacturing, not retrofitted later
- A signed, tested OTA update path treated as core infrastructure
- Data classified by sensitivity before storage architecture is finalised
- An explicit answer to "what can someone do with physical access to this device?"
- Compliance requirements reviewed alongside architecture decisions, not after them
None of this is exciting. It won't show up in a product demo. But the products that avoid painful, expensive security failures are almost always the ones where these decisions were made on purpose, early, by someone whose job was to ask the uncomfortable question before the deadline made it easy to skip.
Bluepixel Technologies builds connected devices across healthcare, industrial, and consumer IoT, and treats security and compliance as architecture decisions, not late-stage checklist items.
Share Article
Linkedin
Facebook
Copy link
Recent Blogs
August 19, 2026
Share Article
Linkedin
Facebook
Copy link